What an AI agent is and what it is not
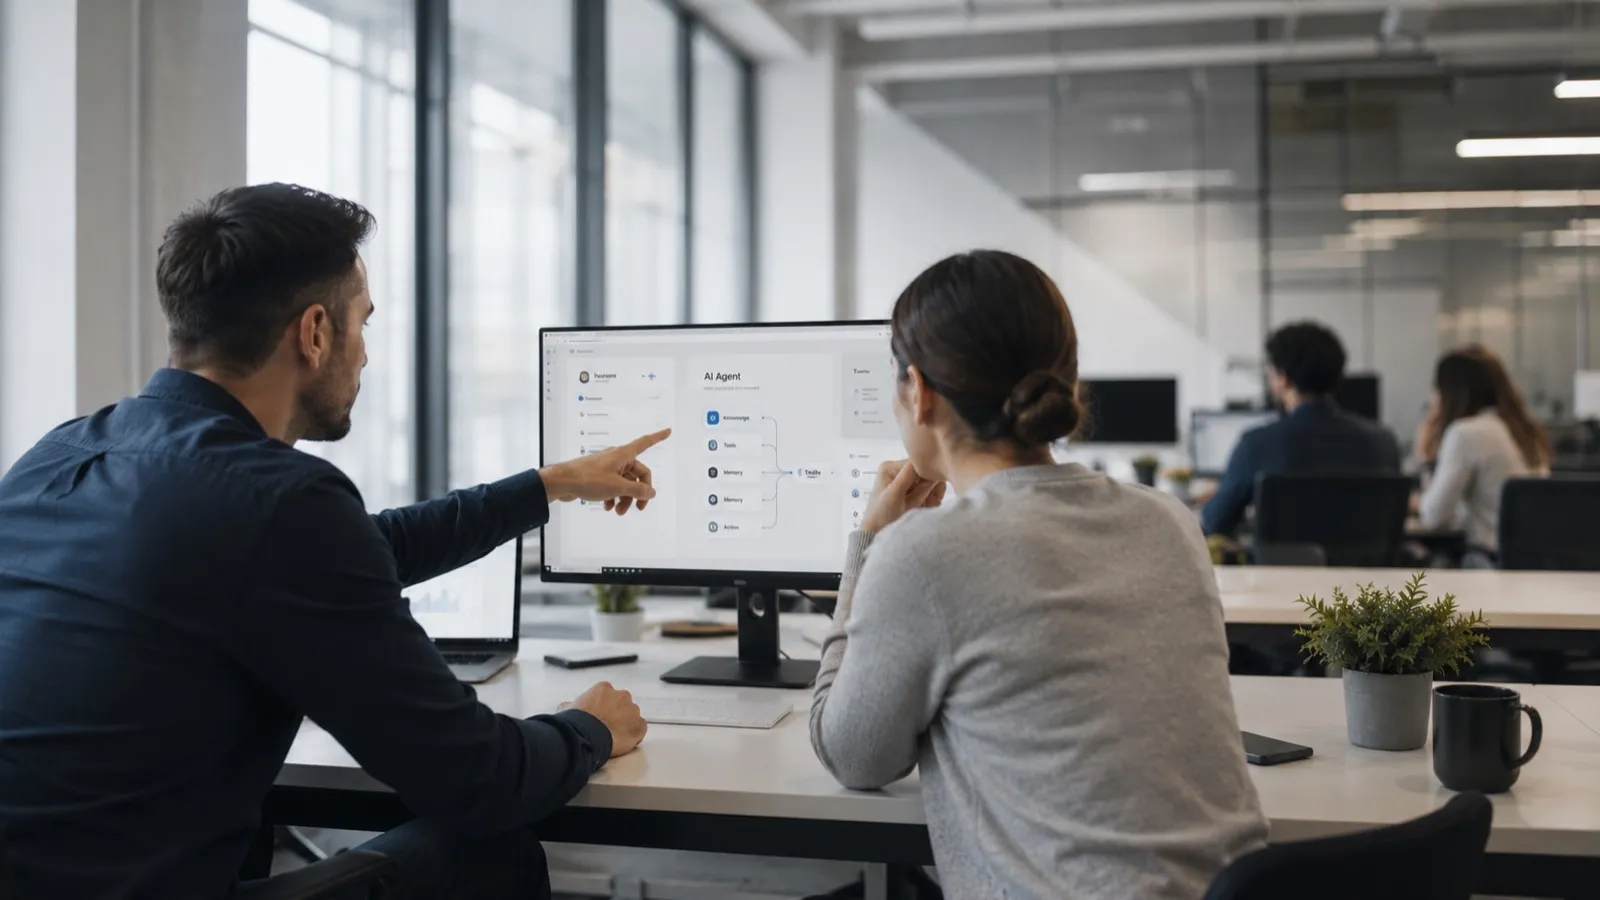
An AI agent is a system that combines a language model with planning capability, access to external tools and context memory. It receives a goal, breaks it down into steps, carries out each step (querying a database, sending an email, updating an ERP) and evaluates the result before continuing. Autonomy is its defining feature: it does not wait for an instruction for each action, but chains decisions together until the process is complete.
It is worth distinguishing it from what it is not. A conversational assistant answers questions, but does not act on other systems. Traditional RPA automation carries out predefined steps, but does not reason or adapt when something goes off script. The AI agent occupies the intermediate and most valuable space: it understands natural language, decides what to do and does it, within the limits the company has set for it.
That final nuance is important. At LurNova we insist that an agent without defined limits is not more intelligent, it is more dangerous. Useful autonomy is governed autonomy: restricted permissions, traceability of every action and human checkpoints where the risk requires them.
How an AI agent works inside
The usual architecture of a business agent has four components. The first is the language model, which acts as the reasoning engine. The second is the planner, the logic that breaks the goal down into tasks and decides the order of execution. The third is the tools: connectors to the company's systems (CRM, ERP, email, databases) that the agent can invoke. The fourth is memory, which allows it to keep the context of a long process and learn from previous interactions.
RAG technology (Retrieval-Augmented Generation) is usually added to this base, connecting the agent to the organisation's documentary knowledge. Thanks to RAG, the agent does not answer from the model's generic knowledge, but from the company's real documents, procedures and data, with verifiable citations. It is the difference between an agent that gives opinions and an agent that consults the right source before acting.
In the agents we develop at LurNova, this architecture is deployed on infrastructure controlled by the client. The reason is practical: if the agent is going to touch internal systems and sensitive data, the company needs to know where each piece of data is processed and who can access the model. Without that traceability, the agent's autonomy becomes a risk that is hard to audit.
What the data say: why 2027 and not later
The figures from the main analysts show a very steep adoption curve. Gartner predicts that up to 40% of enterprise applications will include AI agents for specific tasks in 2026, compared with less than 5% in 2025, according to its press release of August 2025. The same firm estimates that in 2027 a third of agentic AI implementations will combine agents with different capabilities to handle complex tasks.
McKinsey provides the picture of the starting point. Its report The State of AI of November 2025 indicates that 23% of organisations are already scaling agentic systems in at least one business function and another 39% have started experimenting. Adoption is concentrated for now in IT, knowledge management and service operations, which suggests that the remaining functions still have the journey ahead of them.
Deloitte, for its part, predicted in its technology predictions report that 25% of companies using generative AI would launch agentic AI pilots in 2025, a figure that would grow to 50% in 2027. And IDC estimates that agentic AI already accounts for between 10% and 15% of enterprise IT spending in 2026, with a projection of 1.3 trillion dollars of global AI spending by 2029. The same firm predicts in its FutureScape 2026 that, by the end of 2026, 40% of jobs in the large Global 2000 companies will involve direct interaction with AI agents.
There is a nuance worth not losing among so many figures: adoption percentages do not measure maturity. A company having an agent pilot does not mean it has solved governance, integration with its systems or the measurement of return. In fact, the McKinsey report itself notes that, within each specific business function, no more than 10% of organisations are truly scaling agents. The window of opportunity lies precisely there: between 2026 and 2027, the competitive difference will be made not by who experiments, but by who scales with sound judgement.
None of these figures guarantees anything about a particular company. What they do indicate, taken together, is that in 2027 AI agents will be an unavoidable conversation in any management committee: through their own adoption, through competitive pressure or because the software you already use will come with them built in.
The other side: why some of the projects will fail
The same Gartner that anticipates mass adoption warns that over 40% of agentic AI projects will be cancelled before the end of 2027 due to escalating costs, unclear business value or inadequate risk controls. This figure deserves as much attention as the growth figures, because it describes the mistakes we are already seeing repeated.
The first mistake is starting with the technology rather than the process. An agent adds value when it automates a measurable workflow with sufficient volume; if the use case is chosen because it is fashionable rather than for its impact, the return does not come. The second is underestimating governance: an agent that acts on real systems needs defined permissions, action logging and supervision mechanisms from the design stage, not as a later patch. The third is blind dependence on generic platforms, which can leave the company with no control over its data and no ability to audit the agent's decisions.
What we have seen at LurNova with our clients is that the projects that survive share a pattern: a well-defined use case, success metrics defined before starting and an architecture that the company understands and controls. Agentic AI does not fail for lack of technical capability, but for lack of sound judgement in its implementation.
The regulatory factor: what Europe requires and when
The EU AI Act adds a specific timetable to this transition. Since February 2025 the prohibitions on practices of unacceptable risk and the AI literacy obligation have been in force, the latter requiring companies to ensure that their staff have adequate training. Since 2 August 2026 the transparency obligations of Article 50 have also applied, requiring, among other things, that people be informed when they interact with an AI system. An agent that serves customers falls squarely within that obligation.
The most demanding obligations, those for the high-risk systems of Annex III (employment, education, biometrics, critical infrastructure or access to essential services), have been postponed until 2 December 2027 through the Digital Omnibus package, definitively approved by the Council of the EU in June 2026, as set out in the analysis by the law firm Gibson Dunn. This postponement affects neither the prohibitions nor transparency, and it is not an extension to relax: it is time for companies deploying agents in sensitive areas to reach that date with their homework done.
For those implementing AI agents, the practical reading is straightforward. An agent that takes part in decisions about people (shortlisting candidates, assessing credit risk) may fall into the high-risk category and require technical documentation, human supervision and demonstrable traceability. Designing the agent with these requirements from the outset costs much less than reworking it in 2027.
How to prepare your company from today
Sensible preparation does not start with buying technology, but with doing three things. First, mapping processes: identifying which workflows have volume, clear rules and accessible data, because these are the natural candidates for an agent. Second, organising knowledge: an agent with RAG is only as good as the documentation it accesses, and most organisations have that knowledge scattered or out of date. Third, defining the governance model: who authorises which actions, how they are recorded and who reviews the results.
With that foundation, the pilot stops being an experiment and becomes the first step of a strategy. Our usual recommendation is to start with a low-risk internal use case (employee support, document queries, report preparation) and scale towards customer-facing processes only when the organisation has mastered supervision of the agent.
An example illustrates the journey well. An industrial company with thousands of scattered technical documents can start with a RAG-based document query agent: the risk is low, the value is immediate and the project forces it to organise its internal knowledge, which is the basis for everything else. With that infrastructure already in place, the natural next step is an agent that also acts: one that opens incidents, prepares quotes or manages orders with human validation at critical points. Each phase builds on the previous one, and the company learns to govern autonomy gradually instead of facing it all at once.
At LurNova we support this entire journey: from the initial consultancy and the training required by the regulation to the deployment of agents with RAG technology on private models, with our own products such as MIA and LurNova AI Model Hub that allow the company to run its AI without giving up control of its data. Because our premise does not change with fashion: artificial intelligence that is not secure is not intelligent.
Conclusion: 2027 is prepared in 2026
An AI agent is software that reasons, decides and acts autonomously on your company's systems. Data from Gartner, McKinsey, Deloitte and IDC suggest that by 2027 they will be integrated into a large share of enterprise applications, while a significant proportion of projects will fail for lack of governance and sound judgement. And the European timetable sets December 2027 as the deadline for high-risk obligations.
The conclusion is not spectacular but it is useful: the companies that will talk about AI agents in 2027 with results to show are those that in 2026 chose the right use case, organised their data and designed governance from the outset. If you want to assess where to start in your organisation, at LurNova we can help you identify the processes with the greatest return and deploy secure AI agents that are traceable and under your control.
CEO of LurNova, with extensive experience in technology and digital transformation. Involved in developing technology projects and applying artificial intelligence in organisations, he combines technical knowledge with business vision.